One Platform or Two? The Real Cost of Managing iOS and Android Side by Side

One Platform or Two? The Real Cost of Managing iOS and Android Side by Side

Some organizations standardize on Apple. Others run Android across the board. But a significant number of mid-market and enterprise companies end up managing both, often without a deliberate decision to do so. The result is a hybrid mobile environment that doubles the management complexity, splits IT expertise, and creates inconsistent security postures across the device fleet.

Why This Matters

Running iOS and Android side by side isn't just a preference question. It's an operational and security decision with real cost implications. Every additional platform means additional MDM configurations, additional security policies, additional app development and testing, and additional training for IT staff. Common challenges include:


  • Maintaining separate MDM profiles and security policies for each operating system
  • Business applications that behave differently or lack feature parity across platforms
  • IT teams splitting their expertise between two ecosystems instead of going deep on one
  • Inconsistent user experiences that drive more support tickets and workarounds


The Opportunity for Business and IT Leaders

For IT leaders, the platform question isn't about which OS is better. It's about what makes sense for the organization's security requirements, management capabilities, and budget. Organizations that make a deliberate platform decision reduce complexity and improve control. A structured approach enables organizations to:


  • Audit the current device fleet to understand the actual iOS/Android split and why it exists
  • Evaluate total cost of ownership including management tools, support burden, and security overhead
  • Assess which platform better supports the organization's primary business applications
  • Define a platform strategy that balances standardization with legitimate exceptions


How Organizations Can Make a Deliberate Platform Decision

The goal isn't necessarily to eliminate one platform entirely. It's to stop managing two platforms by accident. A practical approach typically includes:


  • Mapping device distribution by department and role to identify where standardization adds the most value
  • Comparing MDM capabilities and costs for single-platform vs. dual-platform management
  • Establishing a preferred platform for new device purchases while accommodating documented exceptions
  • Reviewing the platform strategy annually as device capabilities and organizational needs evolve


Choose Deliberately, Not by Default

The organizations with the cleanest mobile environments are the ones that chose their platform strategy rather than inheriting it. When the decision is intentional, management is simpler, security is stronger, and costs are predictable. That's what a trusted technology partner helps you evaluate.
By Joe Rivkin • September 10, 2026
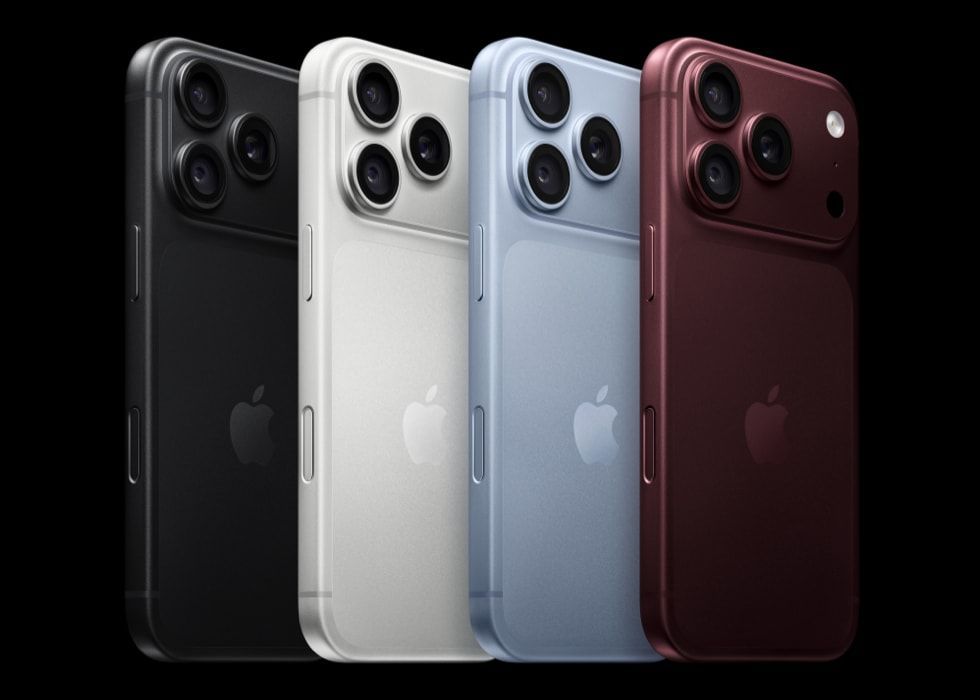
There's No Standard iPhone This Fall. Here's What That Means for Your Business Apple's "Surprise and Shine" event delivered a lineup that caught many businesses off guard. The iPhone 18 Pro starts at $1,199, the Pro Max at $1,299, and Apple's first foldable, the iPhone Duo, at $1,999. The real surprise? There is no standard iPhone 18 this fall. Apple's fall lineup is Pro, Pro Max, and Duo only. Companies planning a mid-tier refresh now face a choice: pay the Pro premium or wait until spring 2027. Why This Matters This changes the math on every device refresh conversation happening this quarter. Pre-orders open September 12, deliveries start arriving September 18, and carrier promotions are already live. IT leaders need to plan now, not after the dust settles. Key considerations include: The entry point for a new iPhone jumped to $1,199 with no mid-tier option available until spring 2027 AT&T and T-Mobile are both offering up to $1,200 in trade-in credits with qualifying devices during launch week Two separate pre-order windows (September 12 for iPhone 18 Pro, October 16 for iPhone Duo) create two planning cycles instead of one eSIM-only models deliver the best battery life (up to 45 hours on the Pro Max), which matters for fleet provisioning decisions The Opportunity for Business and IT Leaders The pricing gap between what's available now and what's coming in spring 2027 creates a window to evaluate the fleet deliberately rather than reactively. A structured approach enables organizations to: Identify which roles genuinely need Pro-tier capabilities now and which can wait for the standard model in spring Lock in carrier trade-in promotions during launch week when the offers are strongest Evaluate whether devices coming off contract right now hit the best upgrade math of the year Plan separately for the iPhone Duo as an executive-tier device, not a fleet device How Organizations Can Plan Around This Launch The absence of a standard model this fall isn't a problem if the refresh strategy accounts for it. A practical approach typically includes: Auditing the current fleet to determine which devices are approaching end of support or contract expiration Segmenting the organization into roles that need immediate Pro upgrades versus those that can hold for spring Engaging carrier reps now to lock in volume trade-in and upgrade pricing before launch-week promotions expire Setting a calendar for the October 16 iPhone Duo pre-order window if executive-tier devices are part of the conversation Plan the Refresh. Don't React to the Launch The organizations that save the most on device refreshes are the ones that planned for the announcement before it happened. When upgrade decisions are part of a strategy rather than a reaction, every dollar goes further. That's what a trusted technology partner helps you build.
By Joe Rivkin • September 1, 2026
Apple Business Manager Isn't Optional Anymore. Here's Why Most mid-market companies issue iPhones and iPads to their teams. Far fewer manage those devices properly. Apple Business Manager gives organizations centralized control over device enrollment, app distribution, and security policies. Yet many IT teams either don't use it or barely scratch the surface of what it offers. As device fleets grow and security requirements tighten, that gap becomes a liability. Why This Matters Without centralized device management, every iPhone and iPad in the organization is essentially operating independently. IT teams have limited visibility into what's installed, what's updated, and whether security policies are being followed. The result is a fleet of devices that looks managed but isn't. Common gaps include: Devices enrolled under personal Apple IDs instead of company-managed accounts No ability to remotely wipe or lock a device if it's lost or an employee leaves App distribution handled manually instead of through a managed deployment pipeline Security policies that vary by device because there's no centralized enforcement The Opportunity for Business and IT Leaders For IT leaders, Apple Business Manager is the foundation for turning a collection of individual devices into a managed, secure fleet. Organizations that implement ABM properly gain control without adding complexity for end users. A structured approach enables organizations to: Enroll devices automatically through zero-touch deployment so they arrive configured and ready Distribute and update business applications centrally without requiring action from each user Enforce security policies consistently across every device in the fleet Maintain a complete inventory of company devices with real-time status and compliance data How Organizations Can Get Started with Apple Business Manager Implementing Apple Business Manager doesn't require replacing devices or disrupting current workflows. It's a layer of management that sits on top of what's already in place. A practical approach typically includes: Registering the organization with Apple Business Manager and linking it to your MDM solution Migrating existing devices from personal Apple ID enrollment to managed enrollment Defining security policies for passcode requirements, encryption, and remote wipe capabilities Training IT staff on the ABM console and establishing processes for onboarding and offboarding devices Manage the Fleet, Not Just the Devices The difference between issuing devices and managing them is the difference between hoping security policies are followed and knowing they are. Apple Business Manager makes that possible at scale. That's what a trusted technology partner helps you implement.
By Joe Rivkin • July 30, 2026
Your Vendors Have Access to Your Network. Do You Know How Much? Every vendor, contractor, and service provider with access to your network represents a potential entry point. Most organizations know this in theory but don't have a clear picture of exactly how many third parties have access, what level of access they have, or whether that access is still necessary. The risk isn't hypothetical. Some of the largest breaches in recent years started through a vendor connection. Why This Matters Third-party access tends to accumulate over time. Vendors are granted access for a project, an integration, or a support agreement, and that access often stays active long after the original need has passed. IT teams inherit vendor relationships from previous administrators without full visibility into what was granted. Common vulnerabilities include: Vendor accounts with access credentials that haven't been reviewed or rotated in years Third-party integrations with broad network permissions that exceed what the service requires Former vendor relationships where access was never formally revoked No centralized inventory of which vendors have access to which systems The Opportunity for Business and IT Leaders For IT leaders, the opportunity is to bring vendor access under the same governance as employee access. Organizations that manage third-party risk proactively reduce their exposure without disrupting the vendor relationships they depend on. A structured approach enables organizations to: Build a centralized inventory of every third party with access to company systems or data Review and right-size vendor permissions based on current business needs, not original agreements Implement access expiration policies so vendor credentials don't remain active indefinitely Require vendors to meet minimum security standards before granting network access How Organizations Can Take Control of Vendor Access Managing vendor access doesn't mean cutting off partners or slowing down operations. It means knowing exactly who has access, to what, and why. A practical approach typically includes: Conducting a third-party access audit to identify all active vendor credentials and permissions Establishing a vendor access governance policy with clear onboarding and offboarding procedures Implementing time-limited access that requires renewal instead of granting permanent credentials Monitoring vendor activity on the network for unusual patterns that could indicate compromised credentials Know Who's In Your Network The organizations with the strongest security posture are the ones that manage vendor access with the same rigor as employee access. When you know exactly who has access and why, you eliminate one of the most common attack vectors. That's what a trusted technology partner helps you build.
By Joe Rivkin • July 30, 2026
The Compliance Deadline Your IT Team Hasn't Planned For Regulatory compliance requirements are expanding faster than most IT teams realize. From CMMC for defense contractors to evolving state privacy laws and SOC 2 expectations from enterprise clients, the deadlines are approaching whether your organization is ready or not. The cost of falling behind is no longer just a fine. It's lost contracts, failed audits, and damaged trust. Why This Matters Compliance used to be a concern for regulated industries like healthcare and finance. That's no longer the case. Mid-market companies across every sector are now being held to security and privacy standards by their customers, partners, and state governments. Common blind spots include: State privacy laws that apply to companies doing business in those states, even without a physical presence Enterprise clients requiring SOC 2 or equivalent certifications before signing contracts CMMC requirements that extend beyond defense contractors to their entire supply chain Cyber insurance applications demanding documented security controls and incident response plans The Opportunity for Business and IT Leaders For IT leaders, the opportunity is to treat compliance as a competitive advantage rather than a burden. Organizations that meet these standards proactively win contracts that competitors can't qualify for. A structured approach enables organizations to: Identify which compliance frameworks apply based on industry, geography, and client requirements Conduct a gap assessment comparing current security controls against required standards Build a remediation roadmap with realistic timelines aligned to upcoming deadlines Document security policies and procedures in a format auditors and clients expect to see How Organizations Can Prepare Before Deadlines Hit Compliance readiness doesn't happen overnight, but it doesn't have to be overwhelming either. The key is starting the assessment early enough to close gaps before they become audit findings. A practical approach typically includes: Running a compliance readiness assessment against the frameworks most relevant to your business Prioritizing remediation based on what auditors and clients check first Implementing security controls that satisfy multiple frameworks simultaneously Establishing a review cadence that keeps documentation current as requirements evolve Compliance as a Competitive Edge The organizations winning the most business today aren't just the most capable. They're the ones that can prove they meet the standards their clients require. When compliance is built into your operations rather than bolted on at audit time, it becomes a differentiator. That's what a trusted technology partner helps you build.
By Joe Rivkin • July 30, 2026
When Your Cloud Provider’s Security Isn’t Enough Most companies assume their cloud provider handles security from end to end. They don't. AWS, Azure, and Google Cloud all operate under a shared responsibility model, where the provider secures the infrastructure and the customer secures everything they put on it. The gap between those two responsibilities is where breaches happen. Why This Matters Cloud providers invest heavily in physical security, network infrastructure, and platform availability. But data configuration, user access controls, and application-level security remain the customer's responsibility. Many IT teams don't fully understand where the provider's coverage ends and theirs begins. Common gaps include: Misconfigured storage buckets or databases left publicly accessible without IT awareness User access permissions that are too broad, giving employees access to data they don't need No monitoring for unusual login patterns or data access from unfamiliar locations Security patches for cloud-hosted applications that are the customer's responsibility, not the provider's The Opportunity for Business and IT Leaders For IT leaders, the opportunity is to map exactly where the cloud provider's security ends and build internal controls to cover the rest. Organizations that take ownership of their half of the shared responsibility model close the gaps that most breaches exploit. A proactive approach enables organizations to: Review shared responsibility documentation for every cloud service in use Audit storage, database, and application configurations for unintended public access Implement identity and access management policies that follow least-privilege principles Deploy cloud security posture management tools that flag misconfigurations in real time How Organizations Can Close the Cloud Security Gap Closing cloud security gaps doesn't mean distrusting the provider. It means understanding exactly what they cover and taking ownership of everything else. A practical approach typically includes: Conducting a cloud security assessment that maps every service against the provider's shared responsibility matrix Establishing configuration baselines and automated alerts for any deviation Training IT staff on cloud-specific security risks that differ from on-premise environments Reviewing cloud security posture quarterly as services and configurations evolve  The Shared Responsibility Model The strongest cloud security postures belong to organizations that stopped assuming the provider handles everything. When you understand exactly where your responsibility begins, you can secure it properly. That's what a trusted technology partner helps you achieve.
By Joe Rivkin • July 13, 2026
Your Data Is Protected at Rest. What About in Transit? Most organizations have invested in protecting stored data. Encryption, backup systems, access controls. These are standard practice. But data doesn't stay in one place. It moves between cloud applications, remote workers, branch offices, and SaaS platforms constantly. And while it's moving, it's often far less protected than when it's sitting still. Why This Matters Data in transit crosses multiple networks, passes through third-party infrastructure, and traverses connections that organizations don't fully control. The rise of remote work and cloud-first strategies means more data is moving across more paths than ever before, and many of those paths weren't designed with security as the primary consideration. Common vulnerabilities include: Data traveling between cloud applications over connections without end-to-end encryption Remote workers accessing sensitive systems through home or public networks API calls between SaaS platforms that transmit business data without adequate authentication Branch office connections that rely on basic VPN without additional security layers The Opportunity for Business and IT Leaders For IT leaders, the opportunity is to treat the data path as a security layer, not just a connectivity layer. Organizations that secure data in motion close one of the most overlooked gaps in their security posture. It's the difference between locking the vault and also securing the truck that carries the contents. A proactive approach enables organizations to: Audit every major data path to identify where sensitive information travels unprotected Implement end-to-end encryption for data moving between cloud services, offices, and remote workers Evaluate SD-WAN and secure connectivity solutions that build security into the transport layer Establish monitoring for data in transit that flags unusual volume, destination, or timing patterns How Organizations Can Secure Data in Motion Securing data in transit doesn't require replacing existing infrastructure. It requires understanding where data moves and ensuring every path has appropriate protection. A practical approach typically includes: Mapping all data flows to identify where sensitive information leaves protected environments Upgrading connectivity between locations to solutions with built-in encryption and security policies Requiring multi-factor authentication for all remote access to business-critical systems Reviewing third-party SaaS connections to verify they meet encryption and authentication standards Protect the Path, Not Just the Destination The companies with the strongest data protection strategies are the ones that secured the journey, not just the storage. When data is protected at every point along the way, the entire security posture gets stronger. That's what a trusted technology partner helps you achieve.
By Joe Rivkin • July 13, 2026
The Network Gaps Your Firewall Can't See Most companies trust their firewall as the first and last line of network defense. It handles perimeter traffic, blocks known threats, and logs connection attempts. But the gaps that create real risk today aren't at the perimeter. They're inside the network, in the spaces between devices, segments, and access points that the firewall was never designed to watch. Why This Matters Networks have grown more complex than perimeter security was built to handle. Remote work, IoT devices, cloud connections, and shadow IT have created internal traffic patterns that bypass the firewall entirely. Attackers know this, and increasingly target the inside of networks where monitoring is weakest. Common blind spots include: Legacy devices still connected to the network with outdated firmware and no security patches Flat network architectures where a breach in one area gives access to everything IoT devices that connect to the network without IT oversight or security configuration Internal lateral movement that firewalls don't monitor because the traffic never crosses the perimeter  The Opportunity for Business and IT Leaders For IT leaders, the opportunity is to extend security visibility beyond the perimeter and into the interior of the network. Organizations that map their internal traffic and segment their networks properly don't just reduce risk; they limit the blast radius when something does go wrong. A structured approach enables organizations to: Identify every device connected to the network, including legacy equipment and unmanaged IoT Implement network segmentation that contains breaches instead of letting them spread Monitor internal east-west traffic for unusual patterns that indicate lateral movement Conduct regular vulnerability scans on internal infrastructure, not just public-facing systems How Organizations Can Close Internal Network Gaps Closing network gaps doesn't require replacing the firewall. It requires complementing it with visibility and controls inside the network. The firewall watches the front door. What most organizations need is someone watching the hallways. A practical approach typically includes: Running a full network discovery to identify every connected device, managed or otherwise Segmenting the network so critical systems are isolated from general-purpose traffic Deploying internal monitoring that detects lateral movement and anomalous device behavior Establishing a review cadence that reassesses network architecture as new devices and services are added Beyond the Perimeter The organizations with the strongest security posture are the ones that stopped assuming the firewall sees everything. When you extend visibility inside the network, you find the gaps before attackers do. That's what a trusted technology partner helps you build.
By Joe Rivkin • July 13, 2026
Your AI Tools Are Learning Fast. So Are the Threats They Attract Companies are adopting AI tools at a rapid pace. What many don't realize is that each new AI integration creates additional entry points, API connections, and data flows that traditional security tools weren't designed to monitor. The attack surface is expanding in real time, and most security postures haven't caught up. Why This Matters AI tools connect to more data sources, generate more API traffic, and process more sensitive information than typical business applications. Each integration creates a potential vulnerability that attackers are already learning to exploit. Security teams built their defenses around a predictable set of tools and traffic patterns. AI changes that equation. Common gaps include: AI integrations with broad data access permissions that were never audited API connections between AI tools and core business systems that bypass traditional monitoring Sensitive data flowing through AI platforms without encryption or access controls Security teams unaware of which AI tools employees have connected to company systems The Opportunity for Business and IT Leaders For IT leaders, the opportunity is to build AI adoption and security posture together rather than bolting security on after the fact. Organizations that assess AI tools through a security lens before deployment avoid the scramble of patching vulnerabilities after they are already in production. A proactive approach enables organizations to: Audit every AI integration for data access scope and API permissions before deployment Establish security review criteria that AI tools must meet before connecting to business systems Monitor AI-generated traffic separately from standard application traffic Create an inventory of all AI tools in use, including those adopted by individual teams without IT approval How Organizations Can Secure Their AI Adoption Securing AI doesn't mean slowing it down. It means treating every AI tool as a new node on the network with its own risk profile. The organizations moving fastest on AI are the ones that built security into their adoption process from the beginning. A practical approach typically includes: Requiring a security assessment before any AI tool connects to company data or systems Implementing network segmentation that isolates AI workloads from critical business applications Deploying monitoring that tracks AI tool behavior and flags anomalies in data access patterns Reviewing AI integrations quarterly as tools update and expand their capabilities Building Secure AI Adoption The companies getting the most from AI are the ones that planned for the risk alongside the reward. When security is part of the adoption process, not an afterthought, organizations can move fast without exposing themselves to threats they didn't see coming. That's what a trusted technology partner helps you build.
By Joe Rivkin • May 26, 2026
Five Questions Every Company Should Ask Before Renewing a Software Contract Most software contracts renew automatically. That is by design. Vendors benefit when companies let renewals pass without review, because it means pricing stays the same, unused licenses stay on the bill, and terms that no longer fit the business stay locked in for another cycle. The renewal window is the one moment where companies have real leverage; yet most let it pass without asking a single question. Why This Matters Software renewals are not just administrative tasks. They are procurement decisions that deserve the same scrutiny as any new purchase. The difference is that by the time a contract auto-renews, the company has already lost its negotiating position. The vendor knows you are staying; the only question is how much you will pay. Common renewal blind spots include: Auto-renewal clauses that trigger 30 to 90 days before the contract end date No internal review of actual usage data before the renewal decision is made Pricing that has not been benchmarked against current market rates or competitor offerings Contract terms written for the company’s needs two or three years ago, not today The Opportunity for Business and IT Leaders For IT leaders, the renewal window is the highest-leverage moment in the software lifecycle. It is the one point where usage data, competitive quotes, and business requirements can all be brought to the table at once. Companies that prepare for renewals consistently pay less, get better terms, and eliminate waste they did not know they were carrying. A structured renewal process enables organizations to: Flag renewal dates 90 days in advance so there is time to review before auto-renewal triggers Pull utilization data to determine whether the current license count and tier still make sense Benchmark pricing against current market rates and request competitive quotes Renegotiate contract terms to reflect how the business has changed since the original agreement Five Questions to Ask Before Every Renewal Before signing off on any software renewal, these five questions should have clear answers. If they do not, the renewal is happening too fast. A practical pre-renewal checklist includes: Are we still using every license we are paying for, or has our headcount or usage changed? Is our current pricing competitive with what the vendor offers new customers today? Have our business requirements changed in ways that affect which features or tier we need? What is the cost of switching versus the cost of renewing on the same terms? Renew on Your Terms The companies that treat renewals as negotiation opportunities instead of calendar reminders are the ones getting better pricing, better terms, and better alignment between what they pay for and what they actually use. That is what a trusted technology partner helps you achieve.
By Joe Rivkin • May 26, 2026
The Hidden Cost Stack: When Software Sprawl Meets Network Sprawl Companies spend a lot of time managing their software costs and a separate amount of time managing their network costs. What they rarely do is look at both together. But every tool in the software stack puts traffic on the network. Every redundant application doubles the bandwidth it consumes. Every unused license still generates background API calls, sync requests, and authentication traffic that the network has to carry. Software sprawl and network sprawl aren’t separate problems. They’re the same problem, compounding. Why This Matters Organizations that manage software and connectivity in silos miss the compounding effect. A bloated software stack doesn’t just cost more in licensing. It costs more in bandwidth, latency, and network infrastructure required to keep everything running. Conversely, a lean software stack on an over-provisioned network means you’re paying for connectivity you don’t need. Common symptoms of the hidden cost stack include: Network performance issues that trace back to excessive SaaS tools running background traffic Bandwidth upgrades driven by software sprawl rather than genuine business growth Software and network budgets managed by different teams with no shared visibility Cost optimization efforts that address one side while the other continues to grow unchecked The Opportunity for Business and IT Leaders For IT leaders, the opportunity is to treat software and network costs as a unified expense category. When both are optimized together, the savings on each side reinforce the other. Fewer tools means less traffic, which means right-sized connectivity, which means lower infrastructure costs. A unified approach enables organizations to: Map the network footprint of each software tool to understand its true total cost Identify tools where the network burden outweighs the business value they deliver Right-size both software licensing and connectivity simultaneously for compound savings Establish a single review process that covers both software and network spending quarterly How Organizations Can Optimize the Full Cost Stack Optimizing the full cost stack starts with visibility across both categories. Most organizations have a software inventory and a network inventory, but they’ve never overlaid one on the other. When they do, the connections between bloated software and strained networks become immediately clear. A practical approach typically includes: Creating a unified view that maps software tools to the network traffic they generate Prioritizing software consolidation based on both licensing cost and network impact Adjusting connectivity plans to reflect actual demand after redundant tools are eliminated Building a quarterly review cadence that evaluates software and network spend together One Stack, One Strategy The companies that treat software and network as one cost stack are the ones finding savings others miss. They’re not just cutting licenses. They’re eliminating the network load those licenses created. And they’re not just upgrading bandwidth. They’re making sure the tools running on it are worth what they cost. That’s what a trusted technology partner helps you see.